


The complete open source phishing framework.
Simulation, AiTM proxy, remote browser phishing and evasion. Built for red teams, organizations and security providers.
Self hosted. Single binary. Open source.
Defensive Make your people
Make your people
harder to phish.
Everything to run your own simulation and awareness programs.
- Phishing simulation Build realistic, multi step phishing and reuse it across campaigns.
- Awareness training Deliver a lesson instead of a lure and track who completes it.
- Reporting Break results down by recipient, department and company, live or exported.
Offensive Break in like
Break in like
a real attacker.
No allowlisting, no special treatment.
- AiTM proxy Relay the real login to capture the live session and get past MFA.
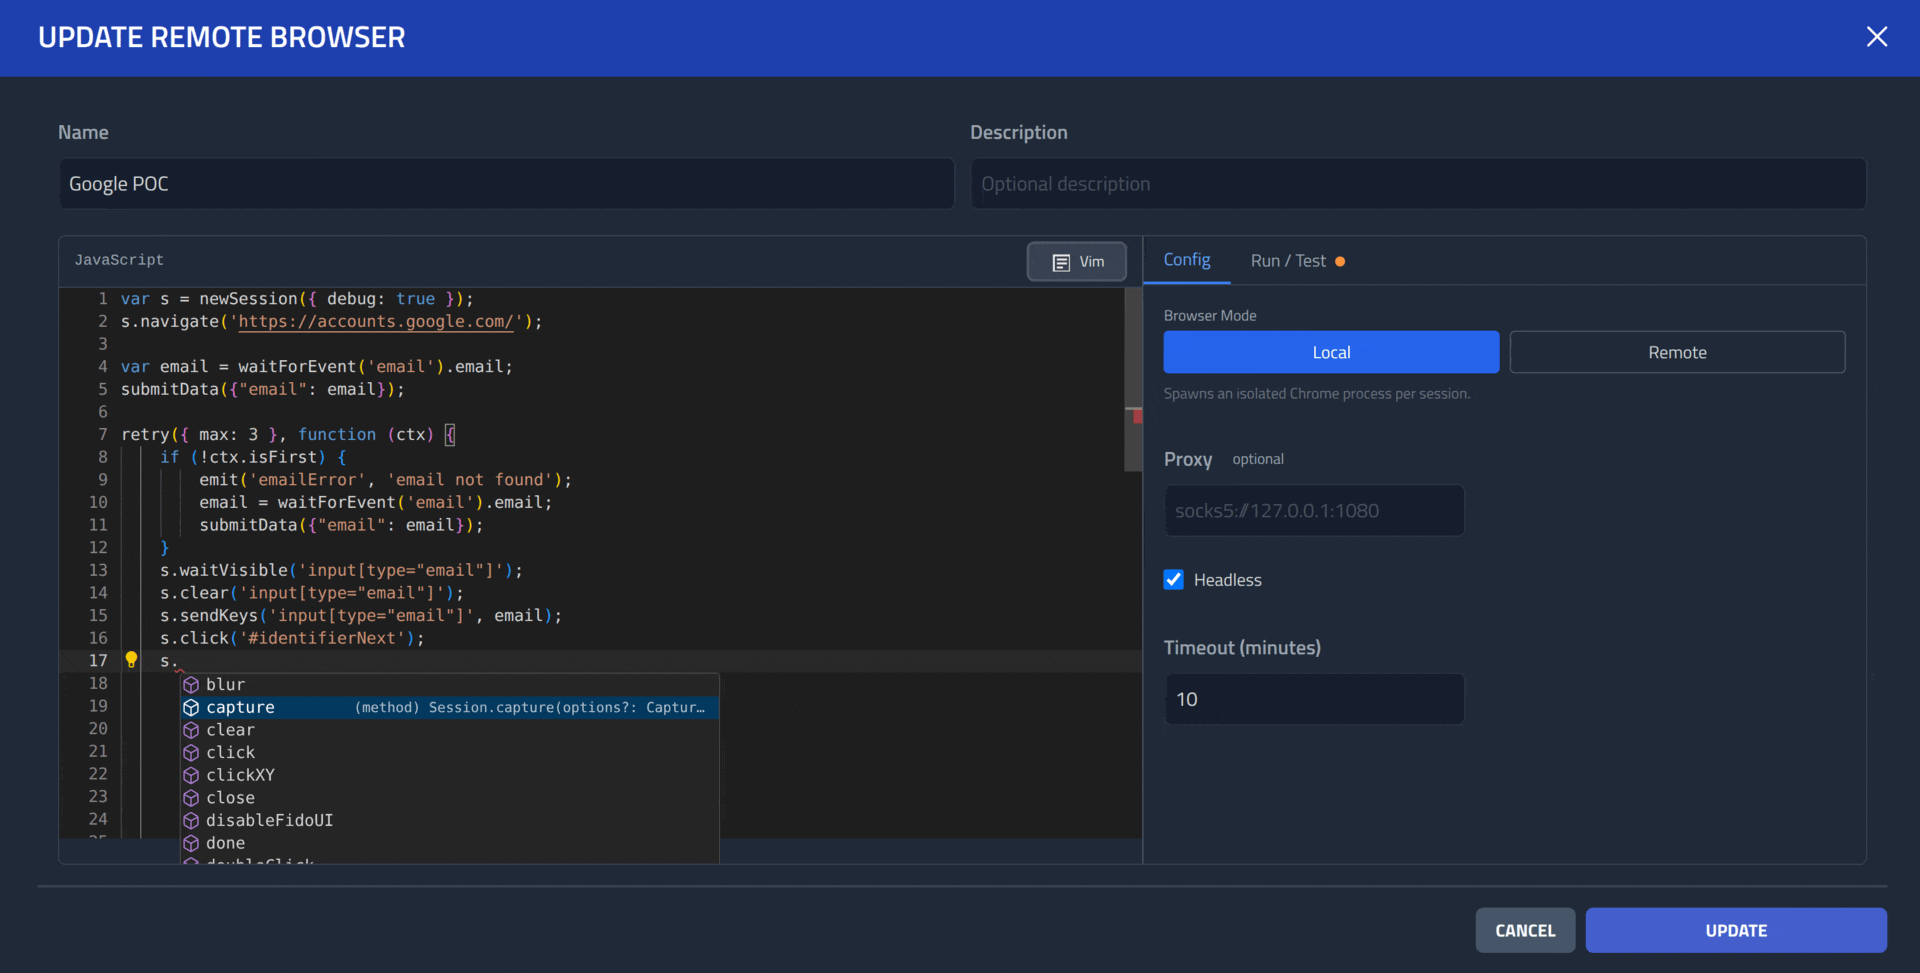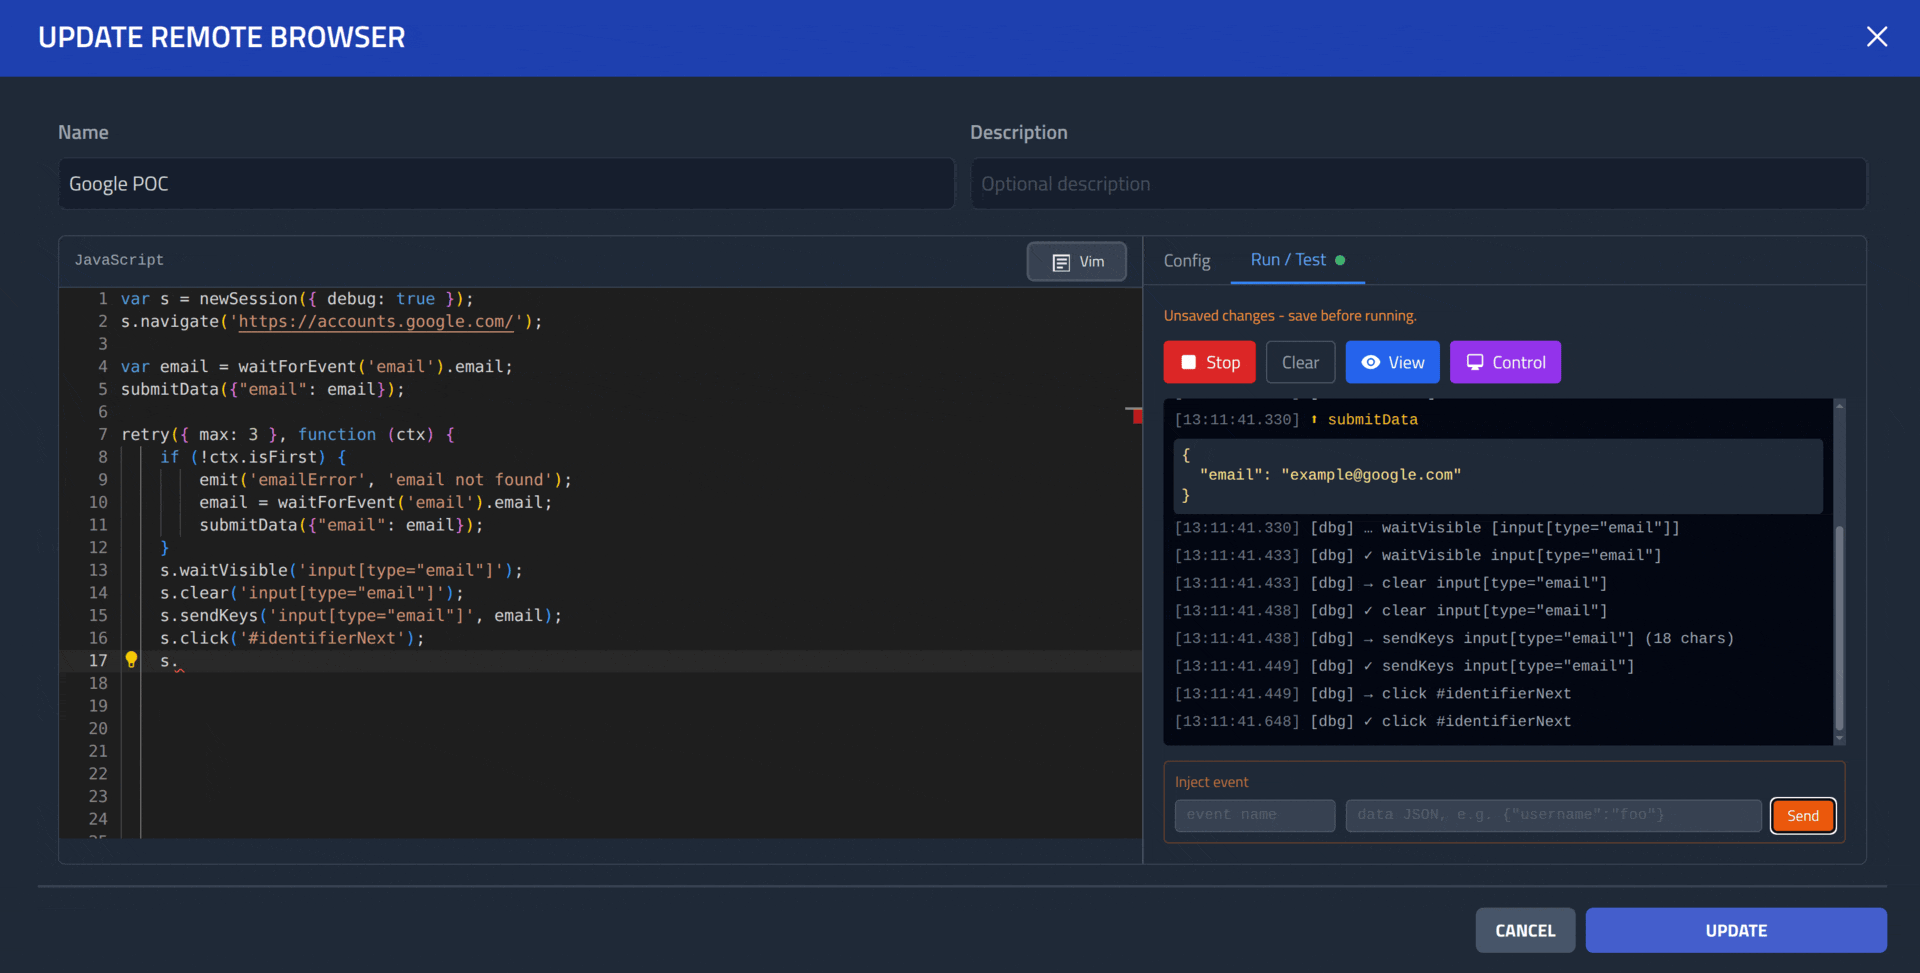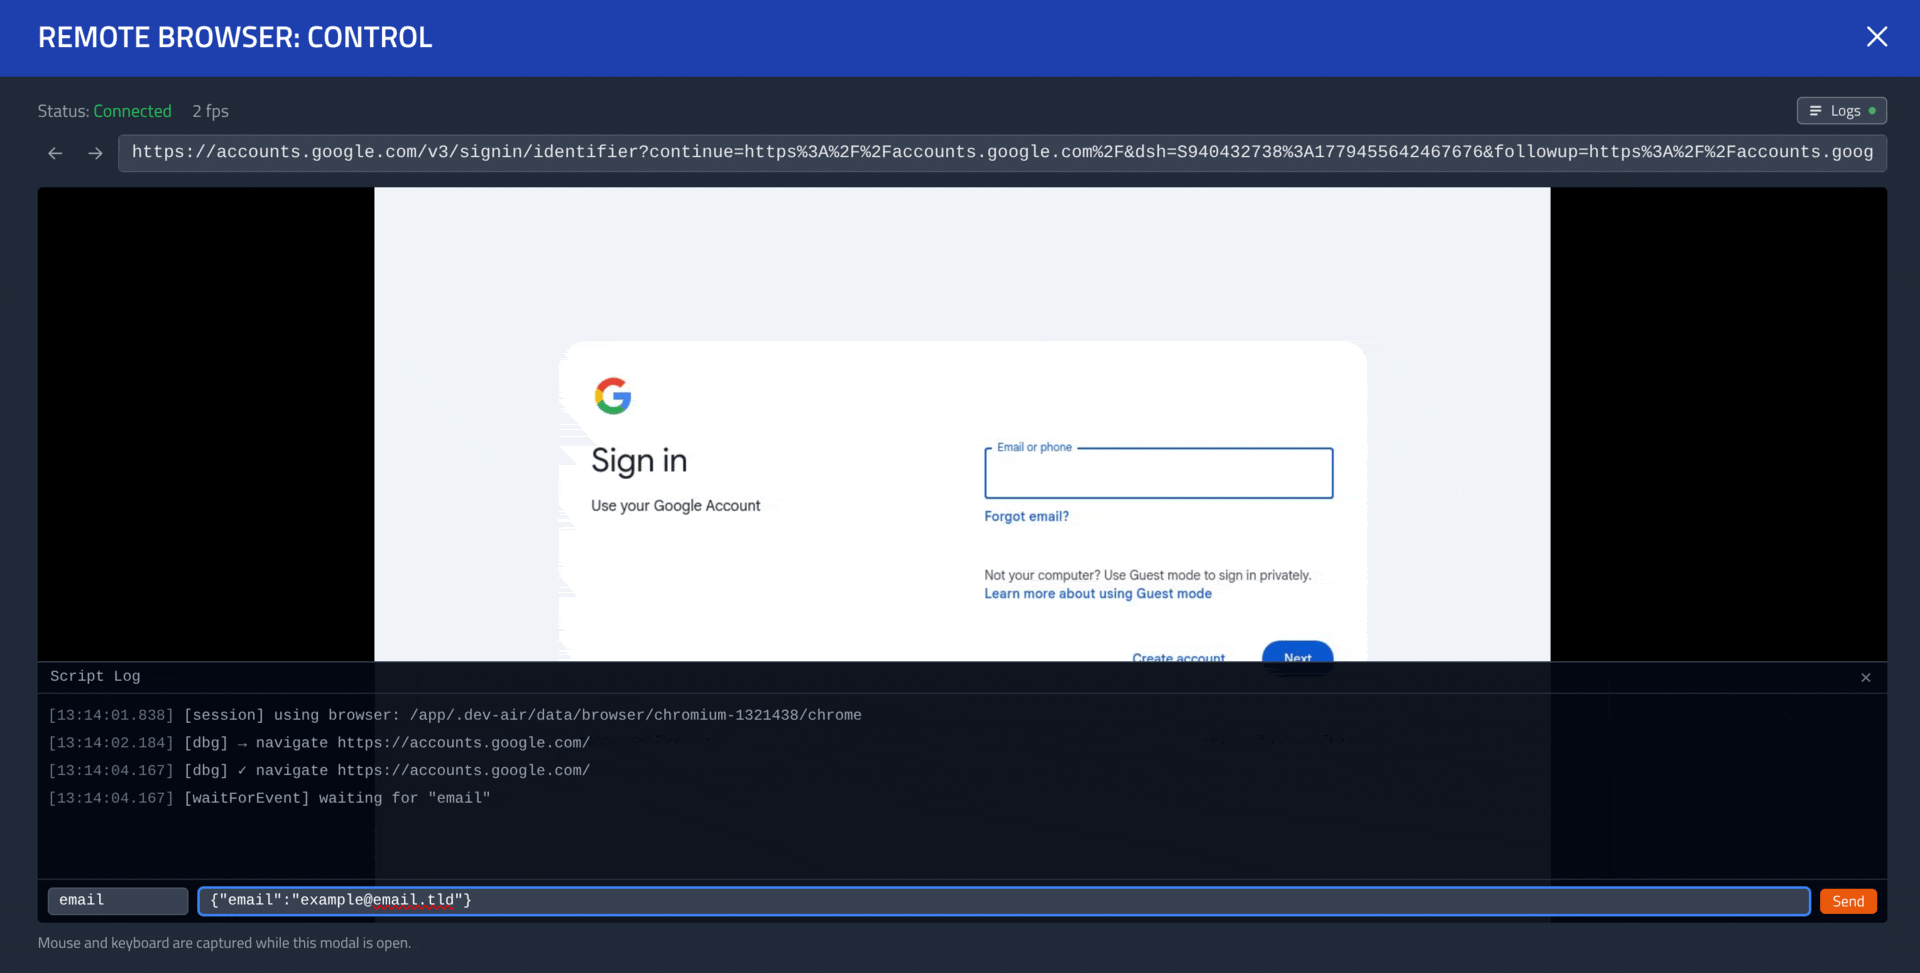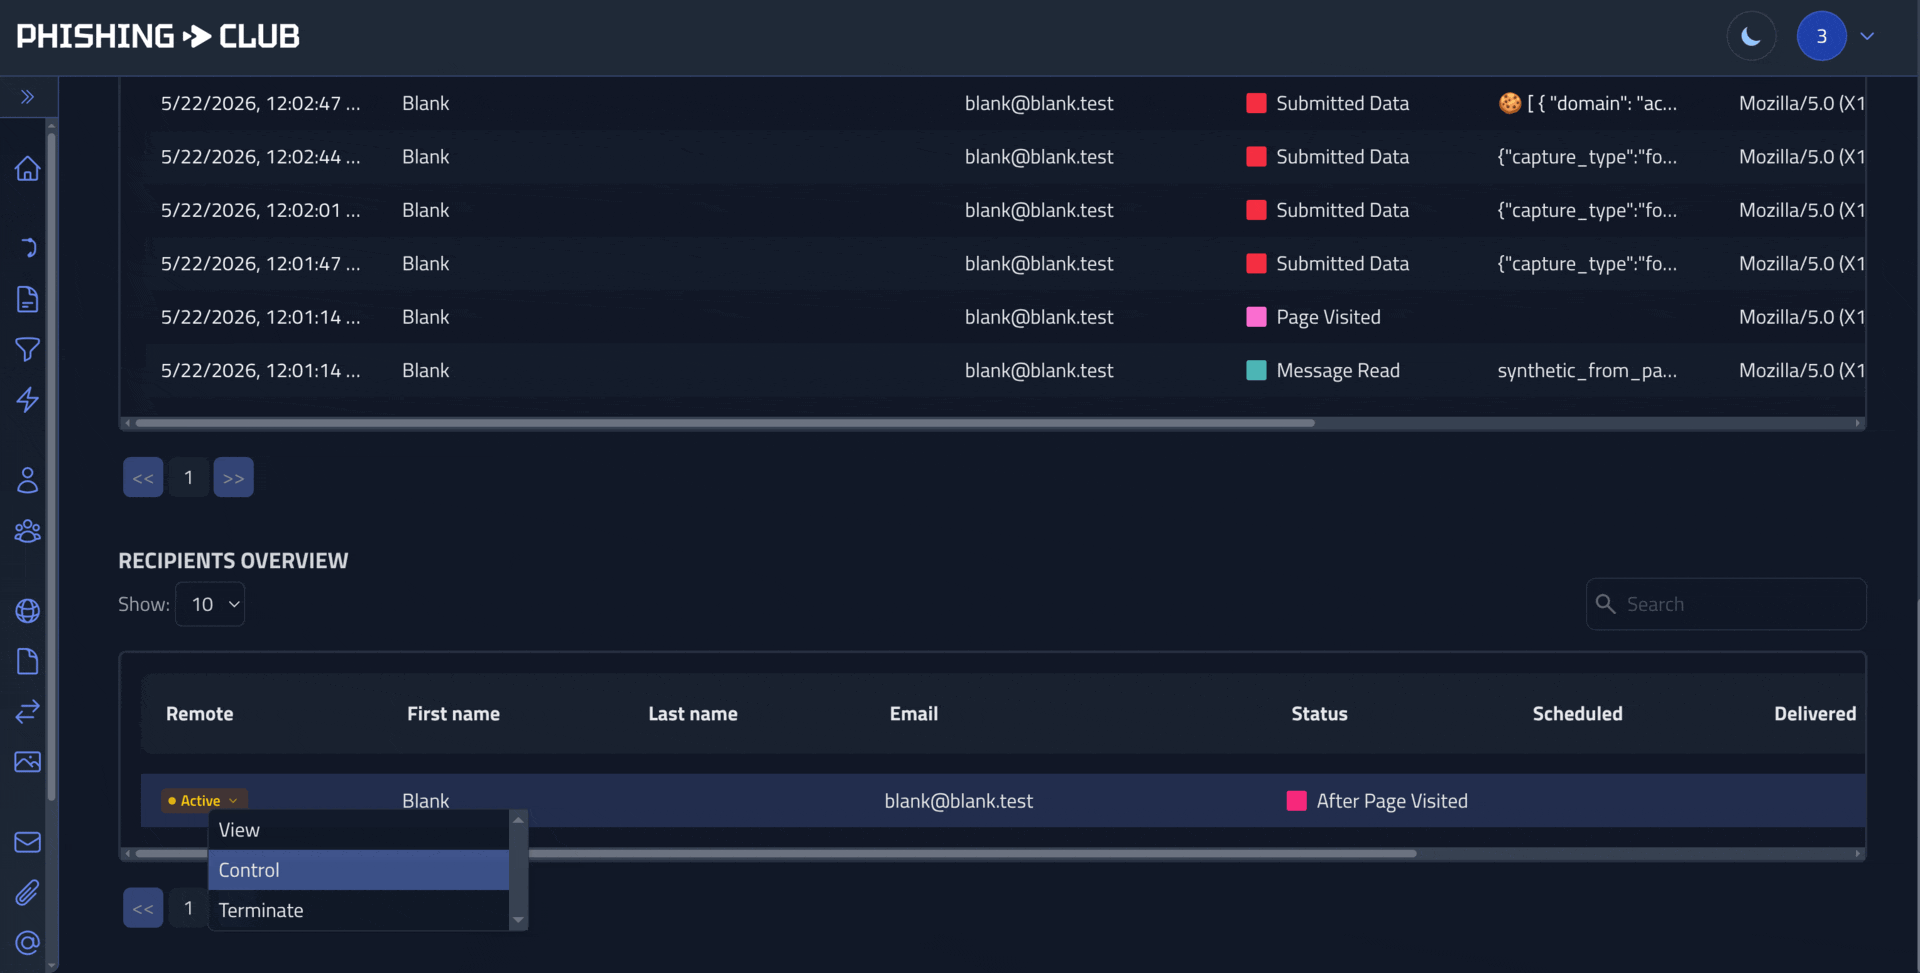
- Remote Browser Phishing Bypass AiTM defenses and device bound cookies, with full control of the page.
- Evasion Filter the lure by IP, ASN, geo and JA4, and obfuscate the HTML on every request.
Feature highlights
Templates & pages
- Email and landing pages in one reusable template
- Chain before, landing and after pages into a multi step flow
- Enrich emails and pages with recipient variables and functions such as dates, random values, QR codes and more
- Write pages in a code editor with code highlighting, VIM support and live split screen preview
Delivery
- Send over SMTP, or your connect via HTTP using the API Sender
- OAuth 2.0 delivery through Microsoft Graph, tokens kept fresh
- Set custom headers and attach files with embedded content
- Send native calendar invites
- Self service: copy rich HTML email content or copy the lure link
- Serve on multiple domains, each with automatic TLS
Recipients & groups
- Import from CSV, or sync using SCIM
- Dynamic groups that filter by attribute and keep themselves current
- Target and personalize on department, position, city and country
- Repeat offenders flagged automatically across campaigns
- See each recipient's full phishing history across every campaign
Scheduling
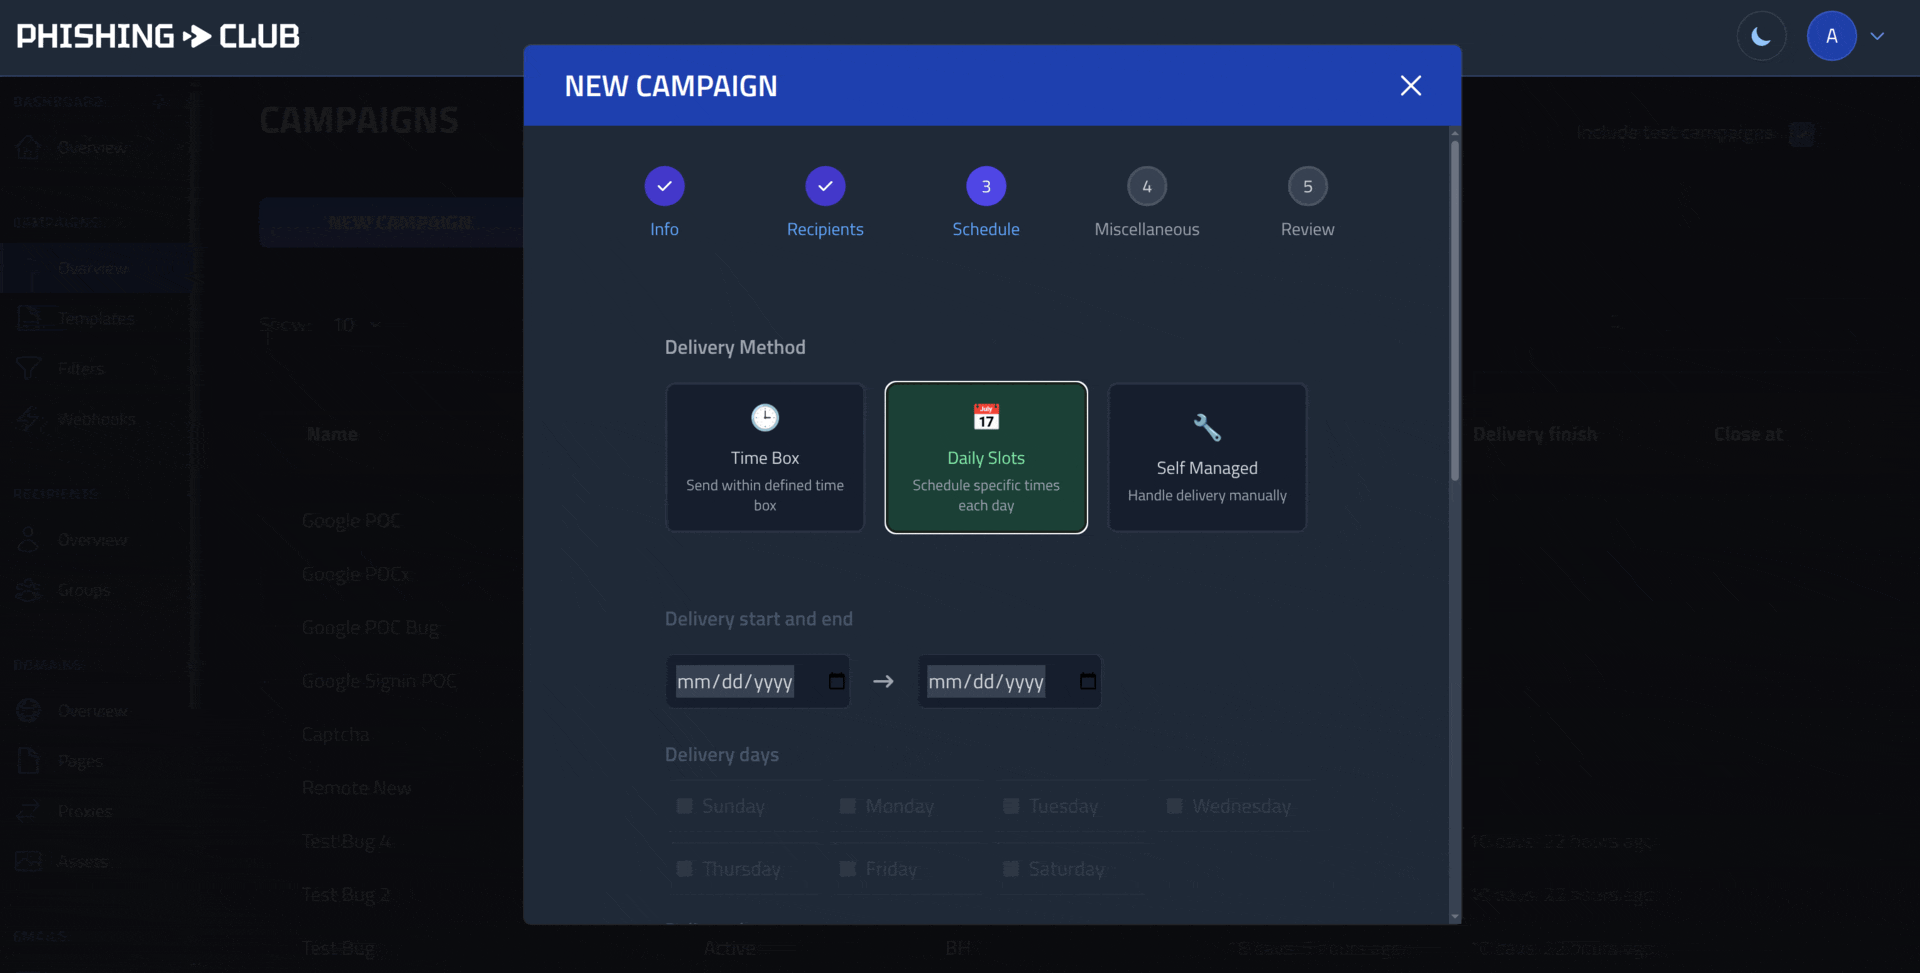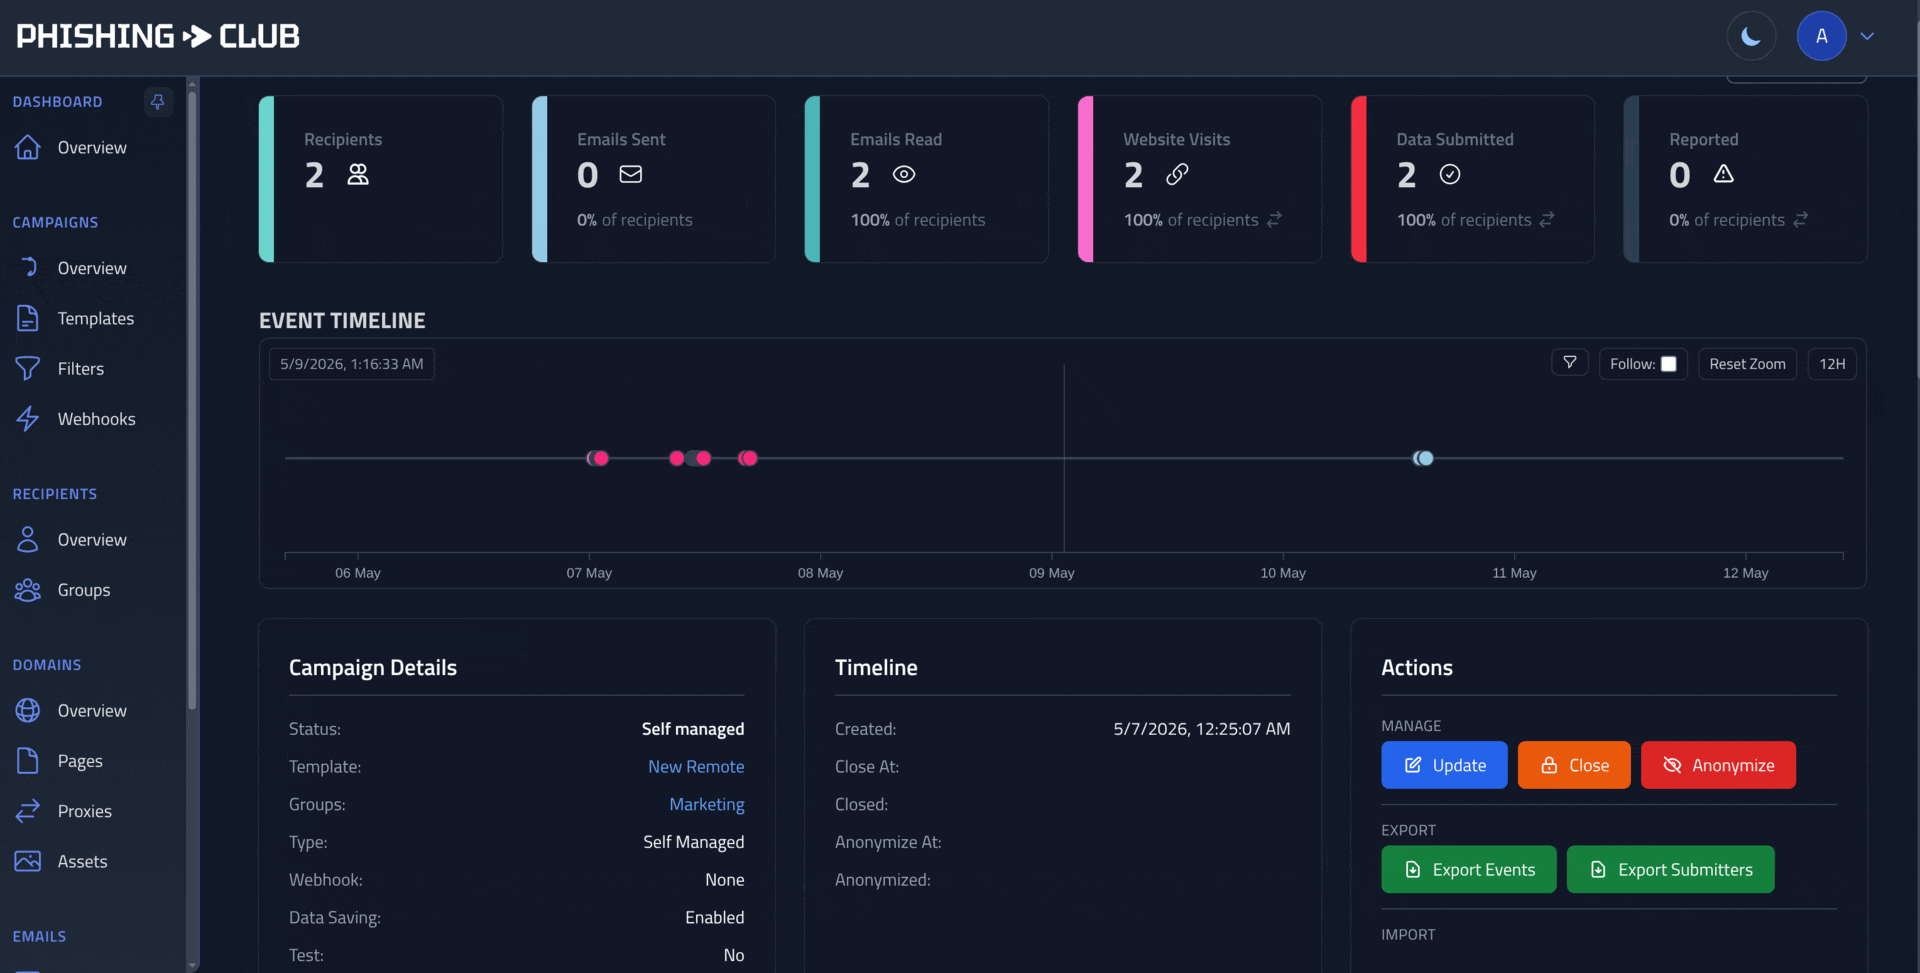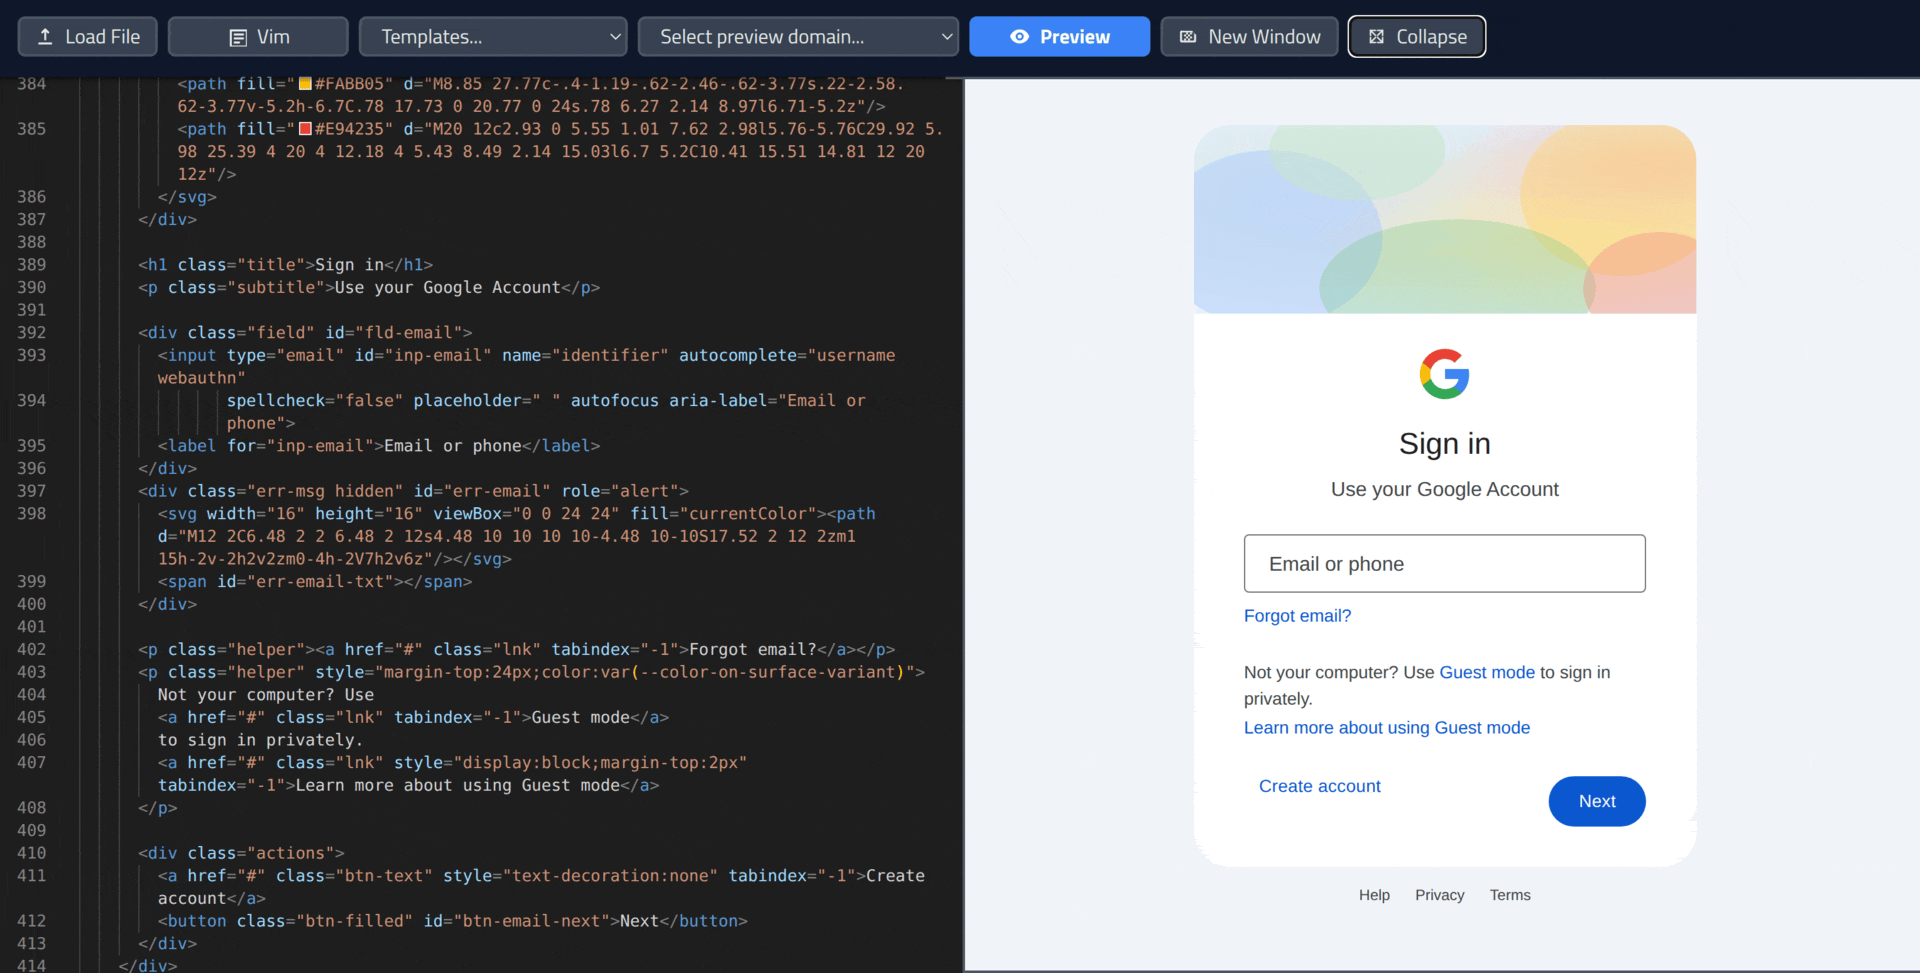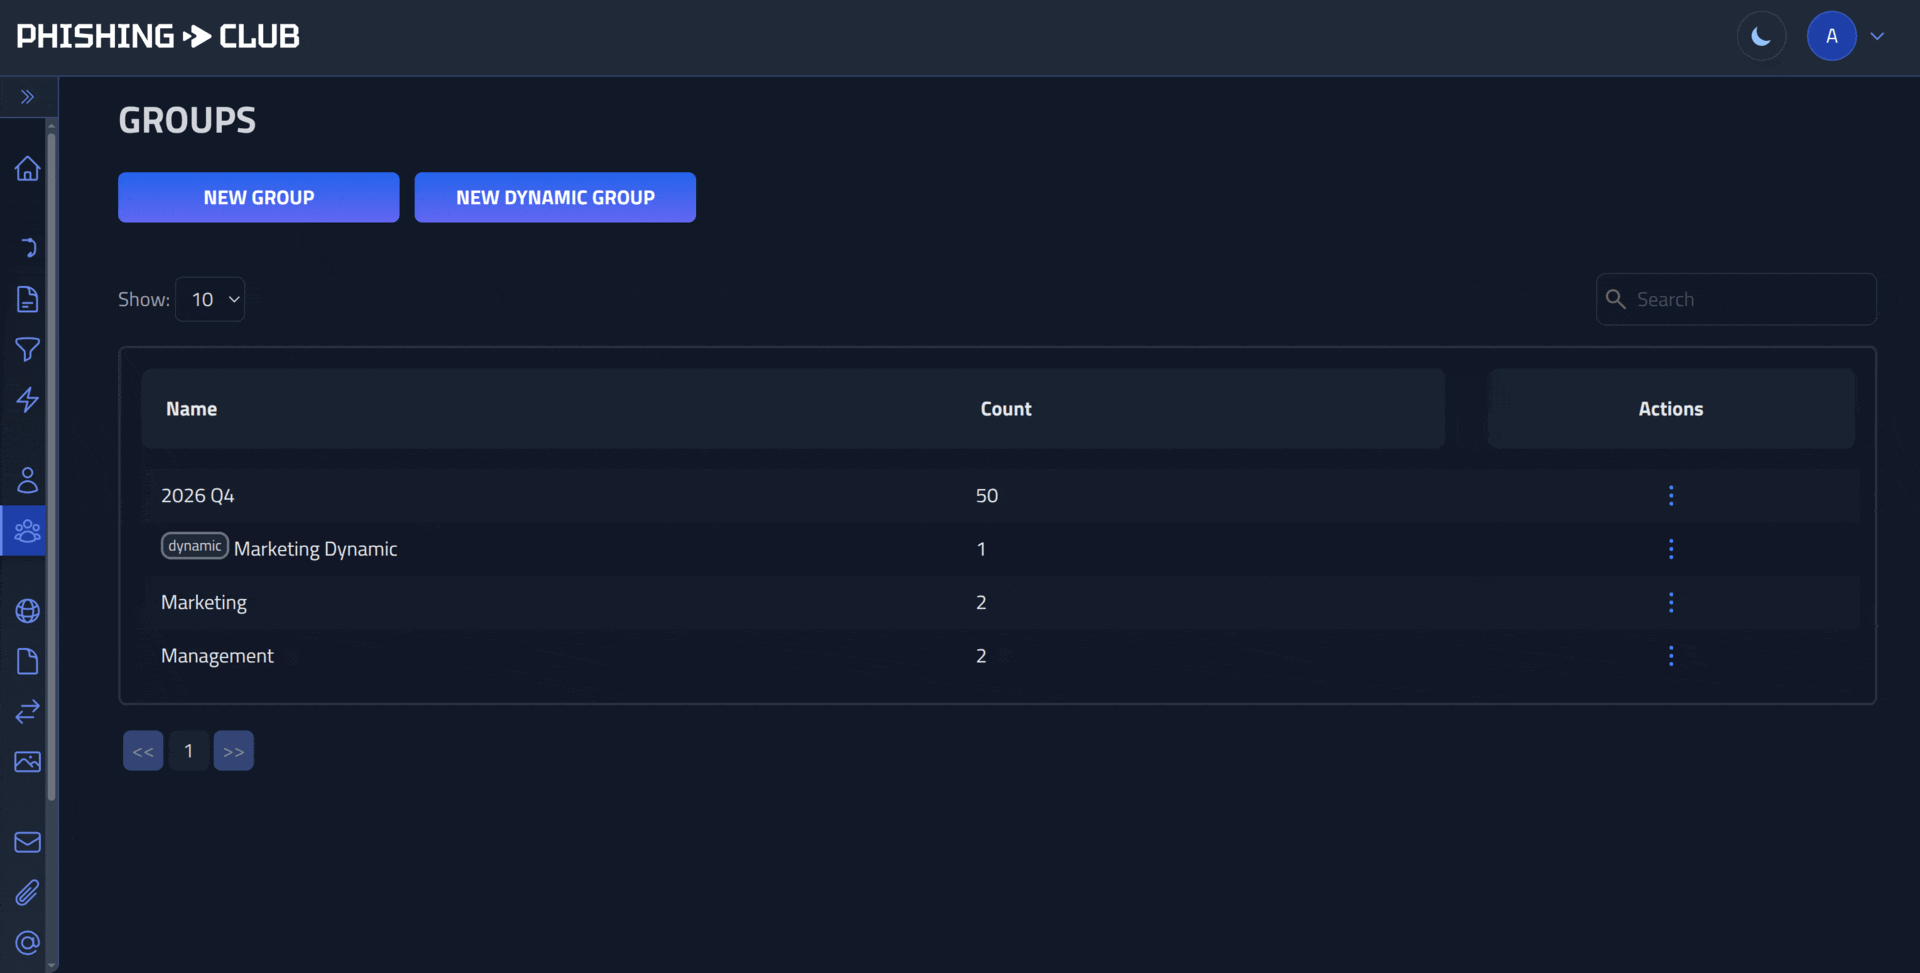
- Spread sends evenly across a time window
- Or hold them to business hours on set weekdays
- Order delivery by department, location or any attribute
- Add random jitter to sending distribution
- Close and anonymize a campaign automatically on schedule
- Resolve the group at campaign send time, so late joiners are included
Awareness training
- Deliver a lesson instead of a lure
- Track who started it and who finished
- Kept out of your phishing risk and repeat offender numbers
- Reuses the same templates, domains and delivery
- Its own reports, emailed when a recipient completes
Analytics & reporting
- Track every open, click, submission and report
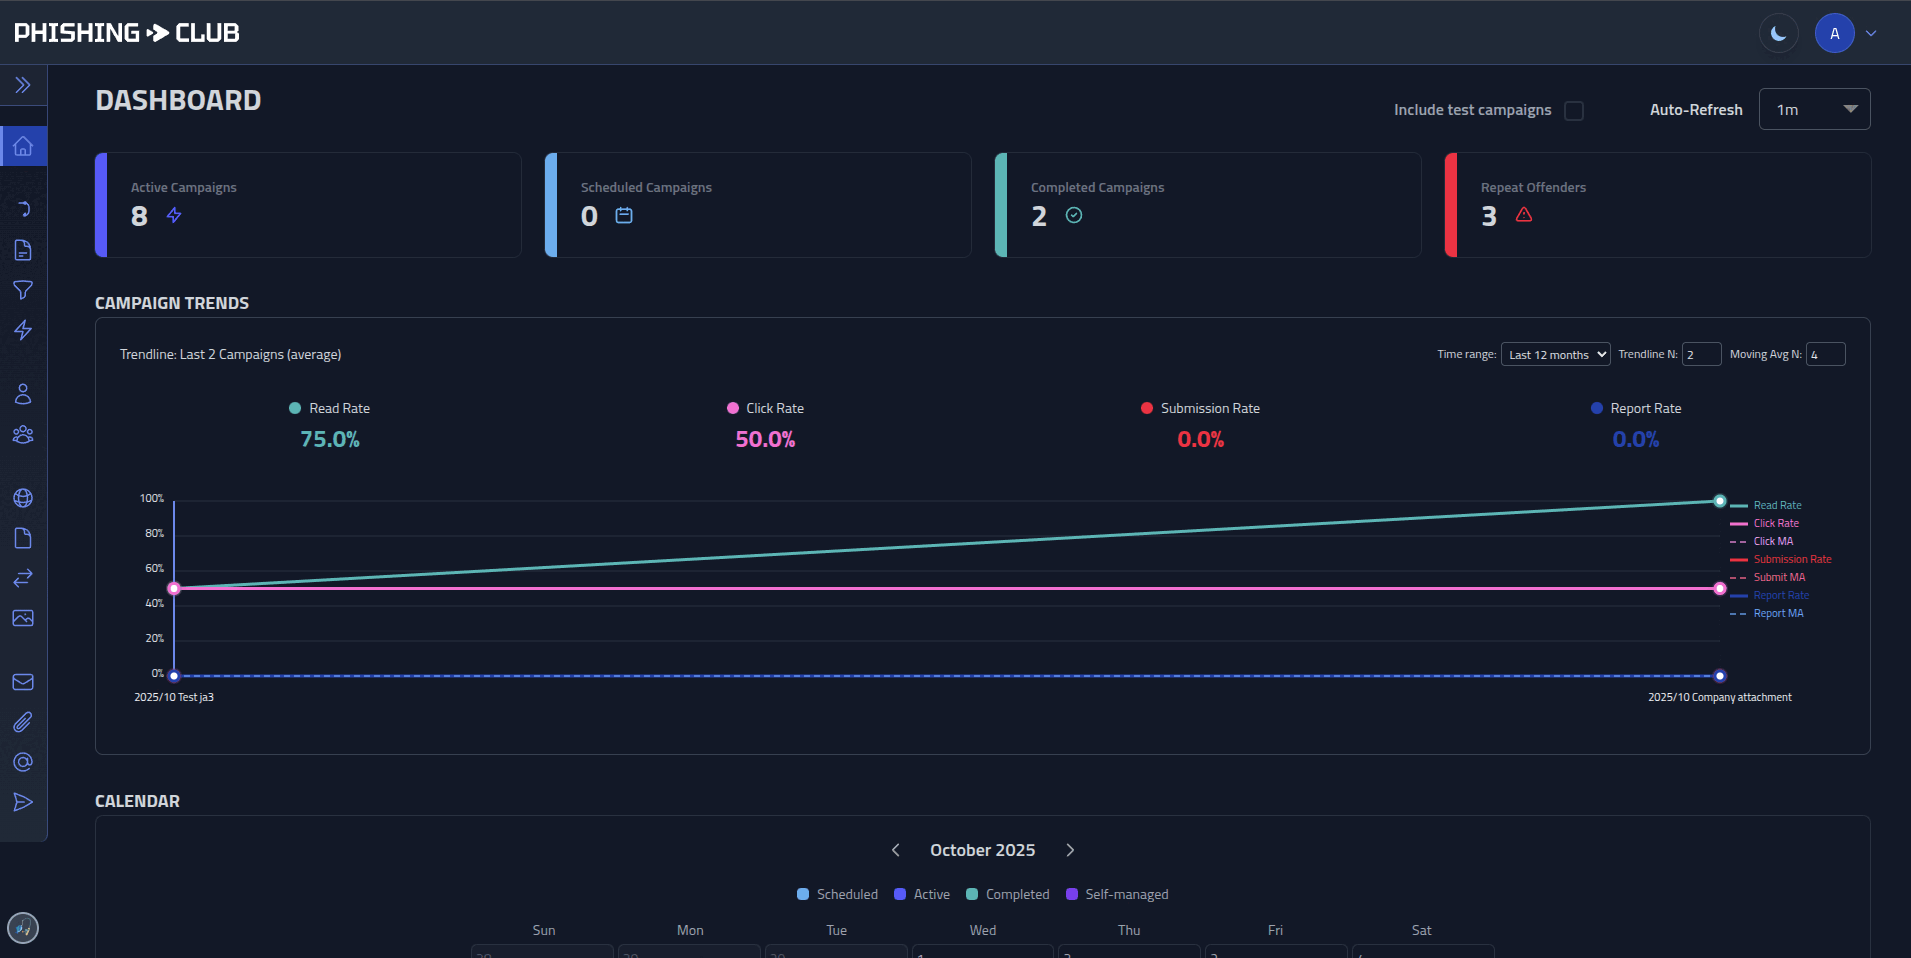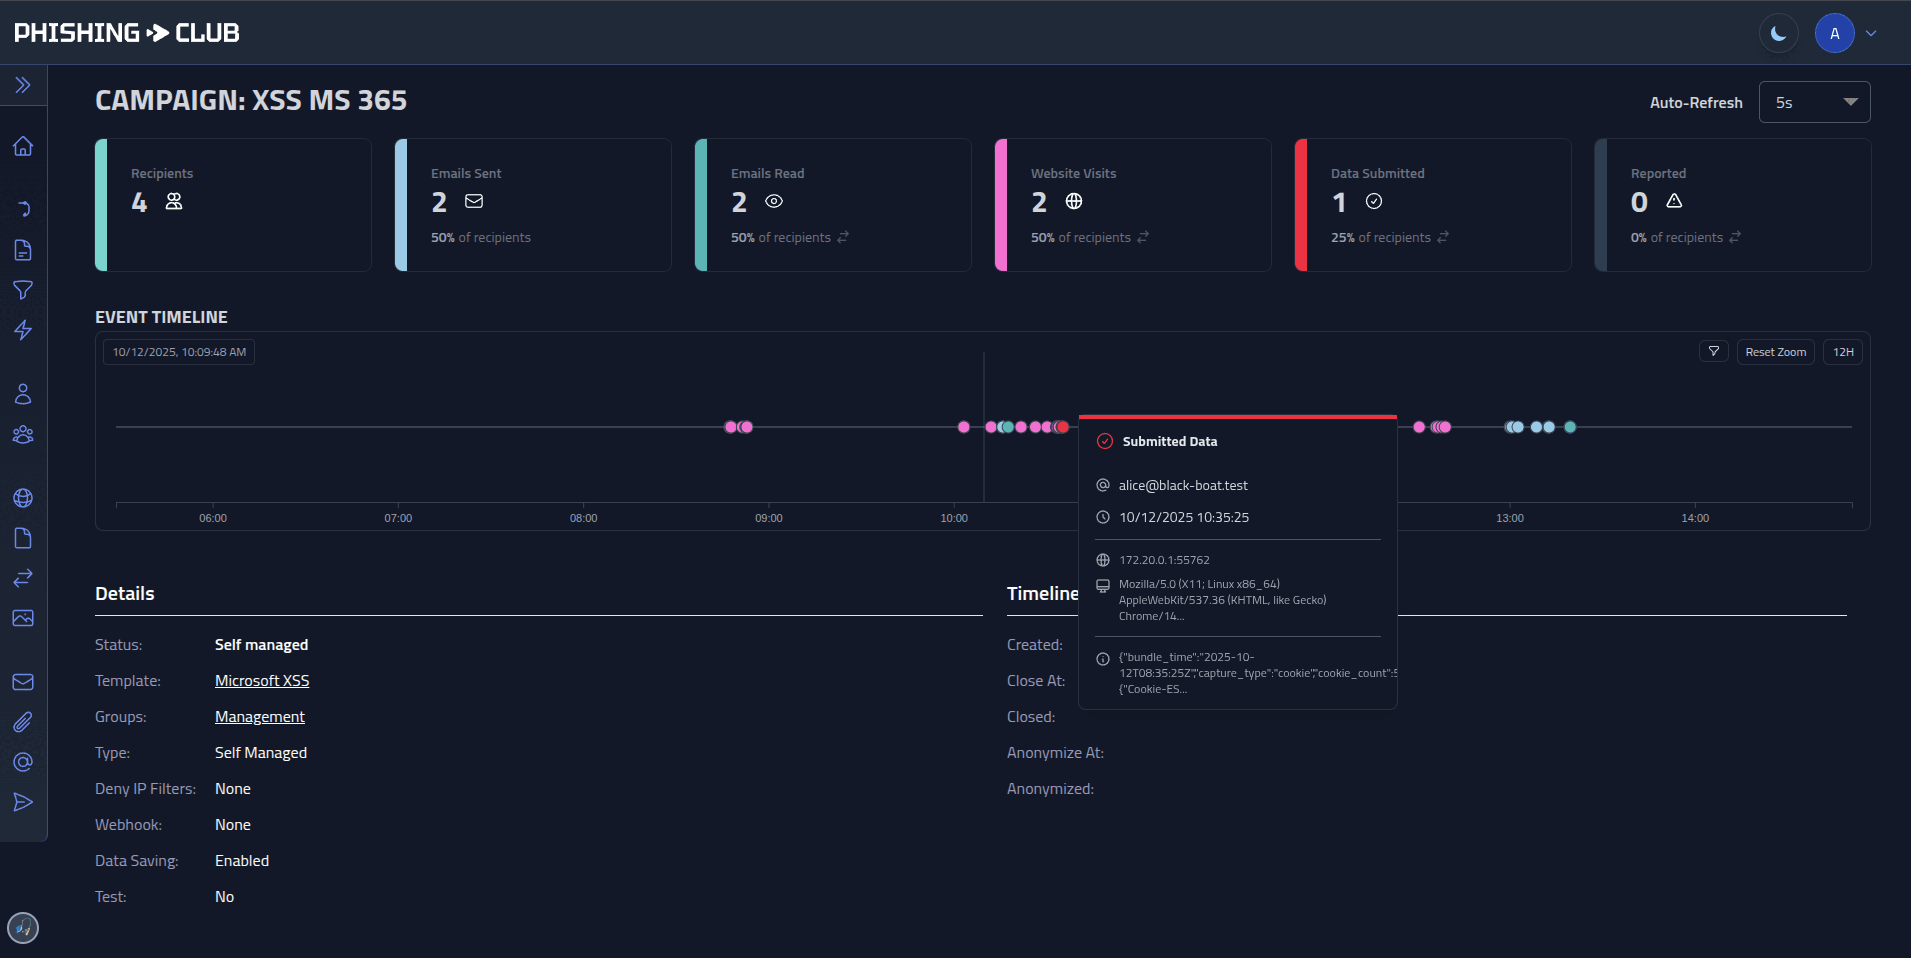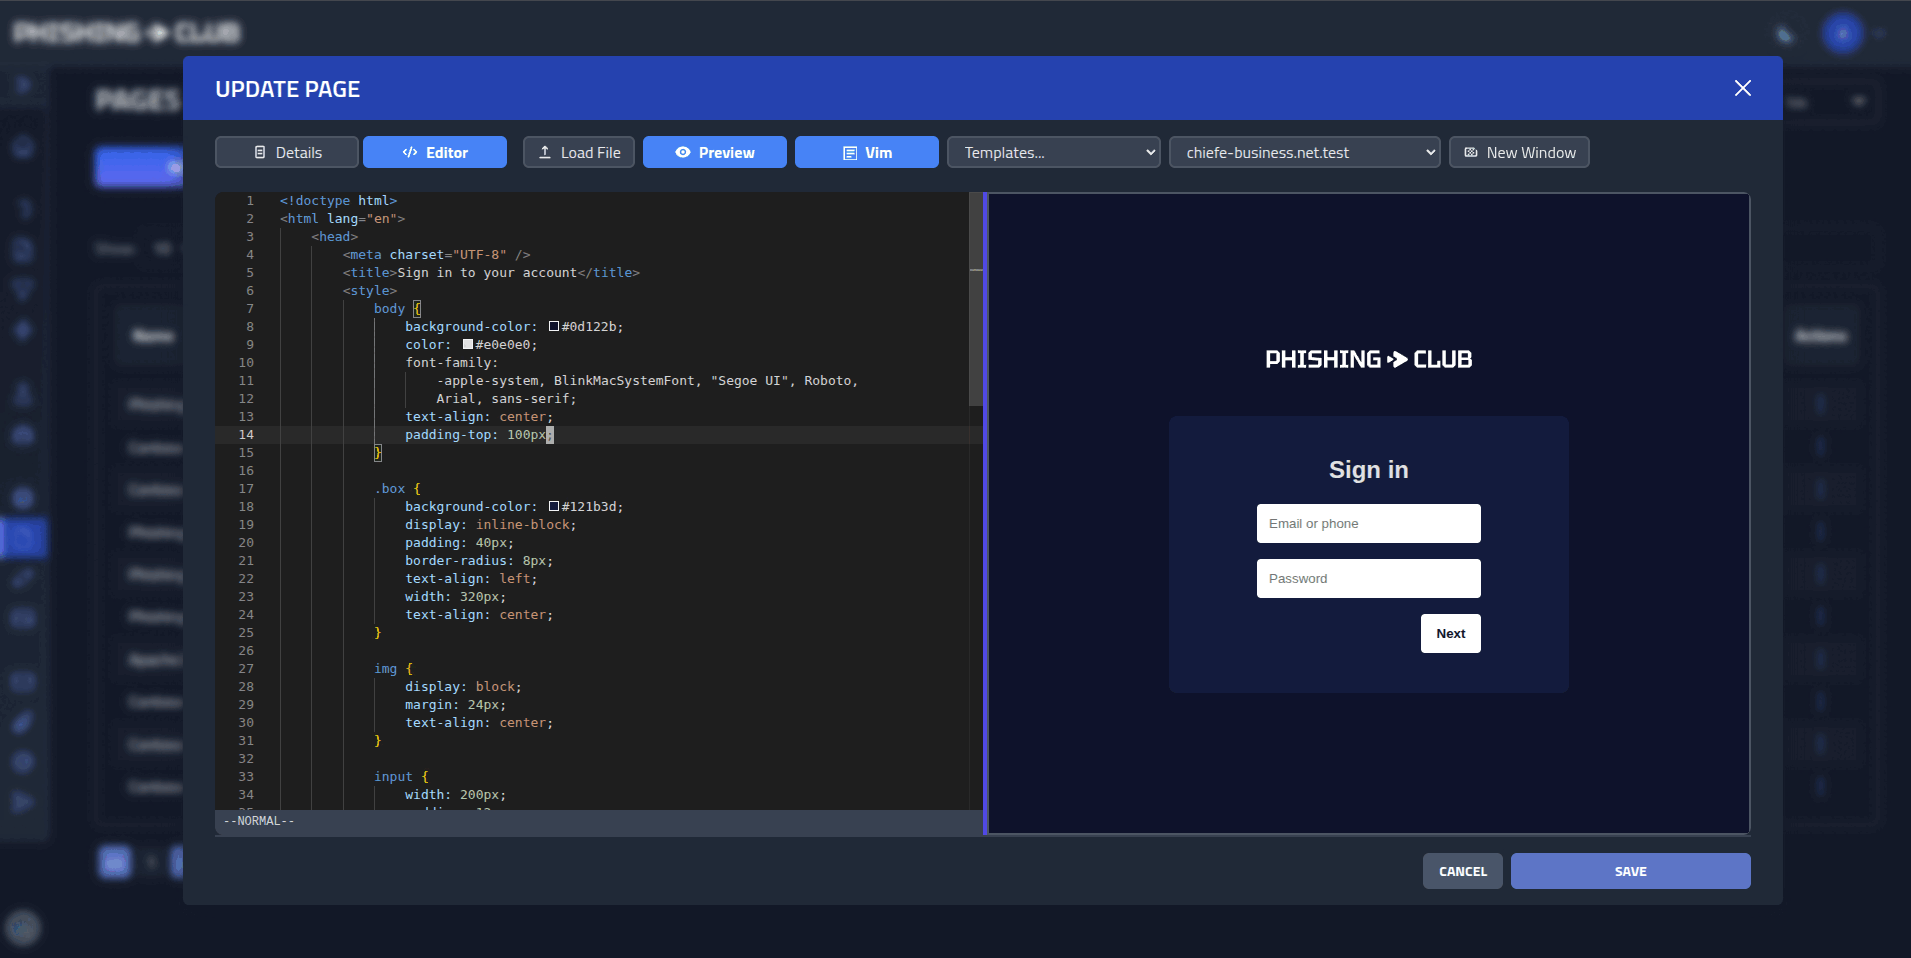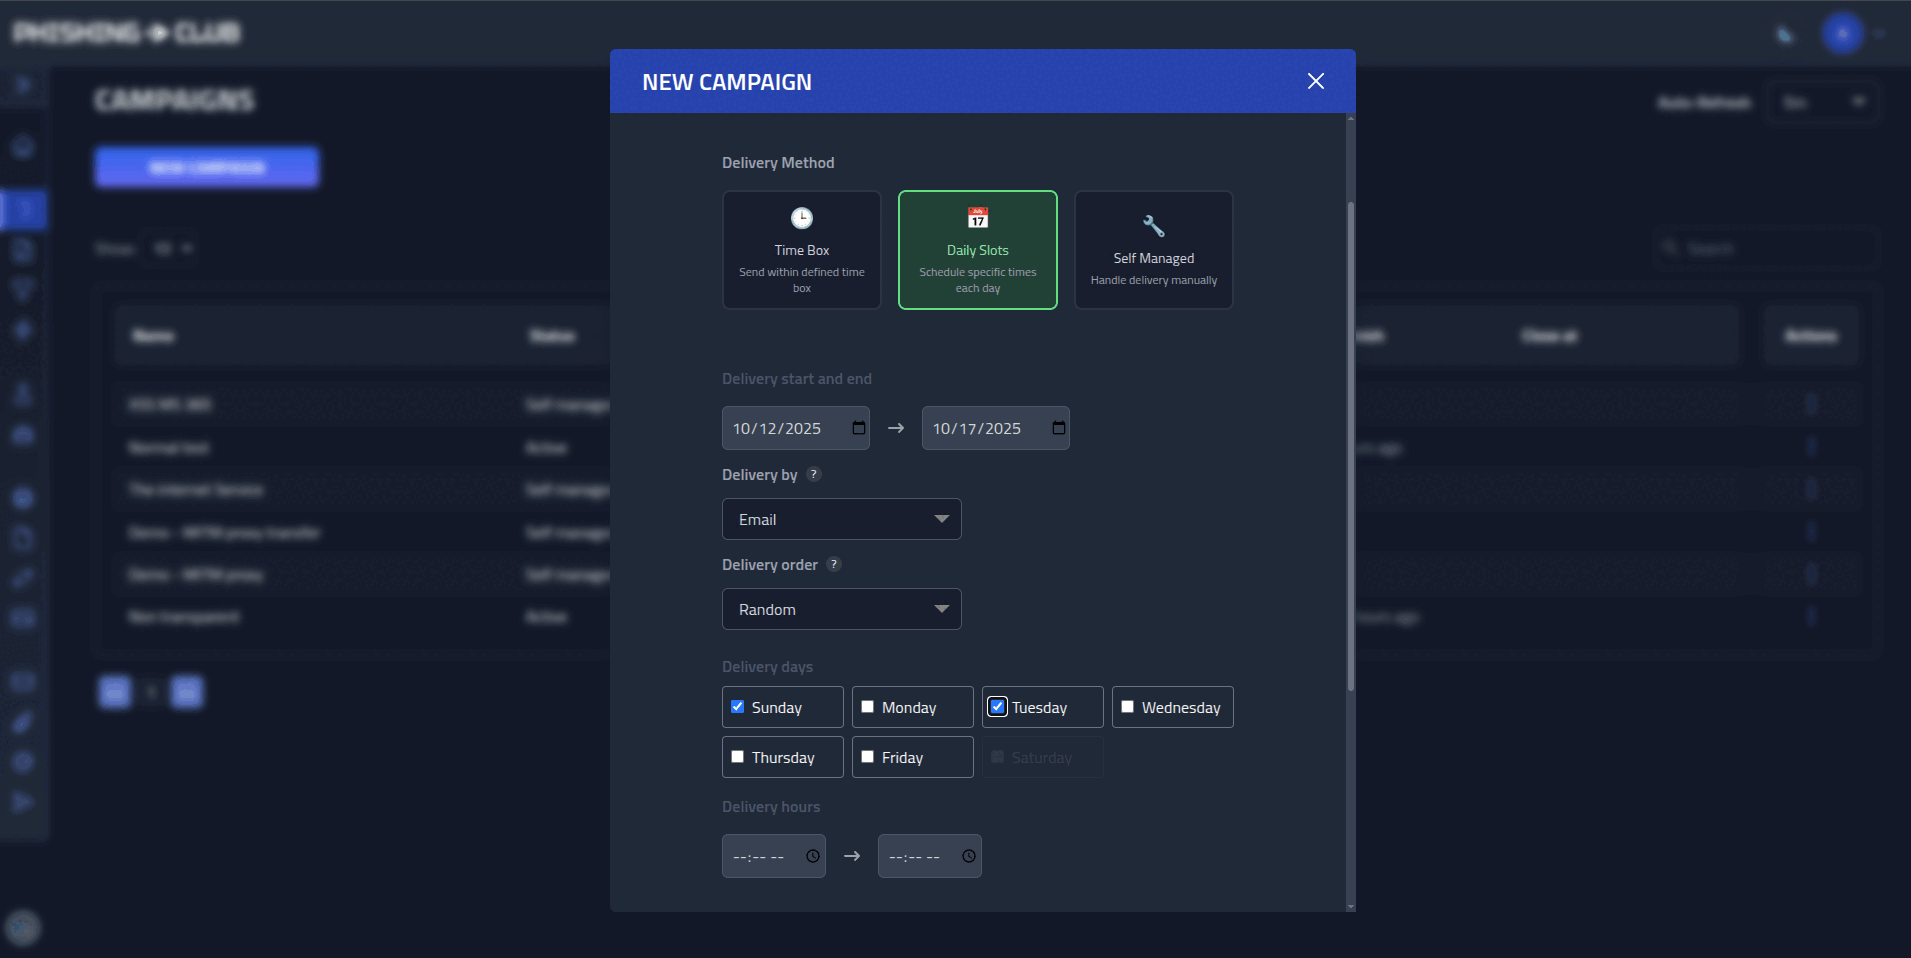
- Follow a campaign live on a timeline and dashboard
- Watch rates trend over time, for phishing or training
- Funnel conversion at each step, to see where people drop
- PDF reports from your own HTML templates, customized per company
- Export every event and submission to CSV
Multi-tenant & privacy
- Run many companies from one instance, with seperate dashboards and more
- Share templates and resources across all of them
- Each company gets its own exports and report templates
- Run anonymous campaigns that never store who did what
- Anonymize on close, with retention limits for compliance
Integration & API
- Webhooks on every event, HMAC signed, with chosen data levels
- REST API with a key per user to automate campaigns
- Session Sushi extension to replay captured sessions in your browser
- Template Workbench to build pages and emails in your own editor
- Import compromised OAuth refresh tokens to keep sending
- Zip import and export, and quick backups
AiTM proxy
- Sit between the victim and the real site to relay the login
- Capture credentials, session cookies and tokens in transit
- Captured sessions bypass MFA that is not phishing resistant
- Rewrite the DOM, headers and URLs on every request
- Impersonate a real browser's JA4 fingerprint to avoid detection
- Route traffic through upstream SOCKS5 or HTTP proxies
- Build it in YAML or a visual builder
Remote browser phishing
- Run the real login in a browser on your server, over CDP
- The victim only ever sees a phishing page you designed
- Beats AiTM defenses and device bound session cookies
- Script the flow: wait for MFA, intercept and automate each step
- Monitor and take over live sessions from the operator panel
Evasion & filtering
- Allow or deny who reaches the lure by IP, country, ASN, JA4 or header
- Custom anti bot client page
- Turn scanners and sandboxes away before they see anything
- Show a custom deny page to anyone blocked
- Customizable obfuscation the page on every request to defeat static detection
Scripts
- Run server side JavaScript, saved and reused
- React to any campaign event as it fires
- Decide what each proxy or remote browser session does, per visitor
- Call external APIs and transform data in code
- Write and test it in a built in editor
- Use to set upstream proxies depending on the visitors geo location

Self hosted. Open source. Free!
Single binary for AMD64 and ARM64. Docker images available.
In app update notifications with one click updates.
Your data stays on your infrastructure.
Free and open source under AGPL v3.
Deployment Single binary
Architecture AMD64 + ARM64
License AGPL v3